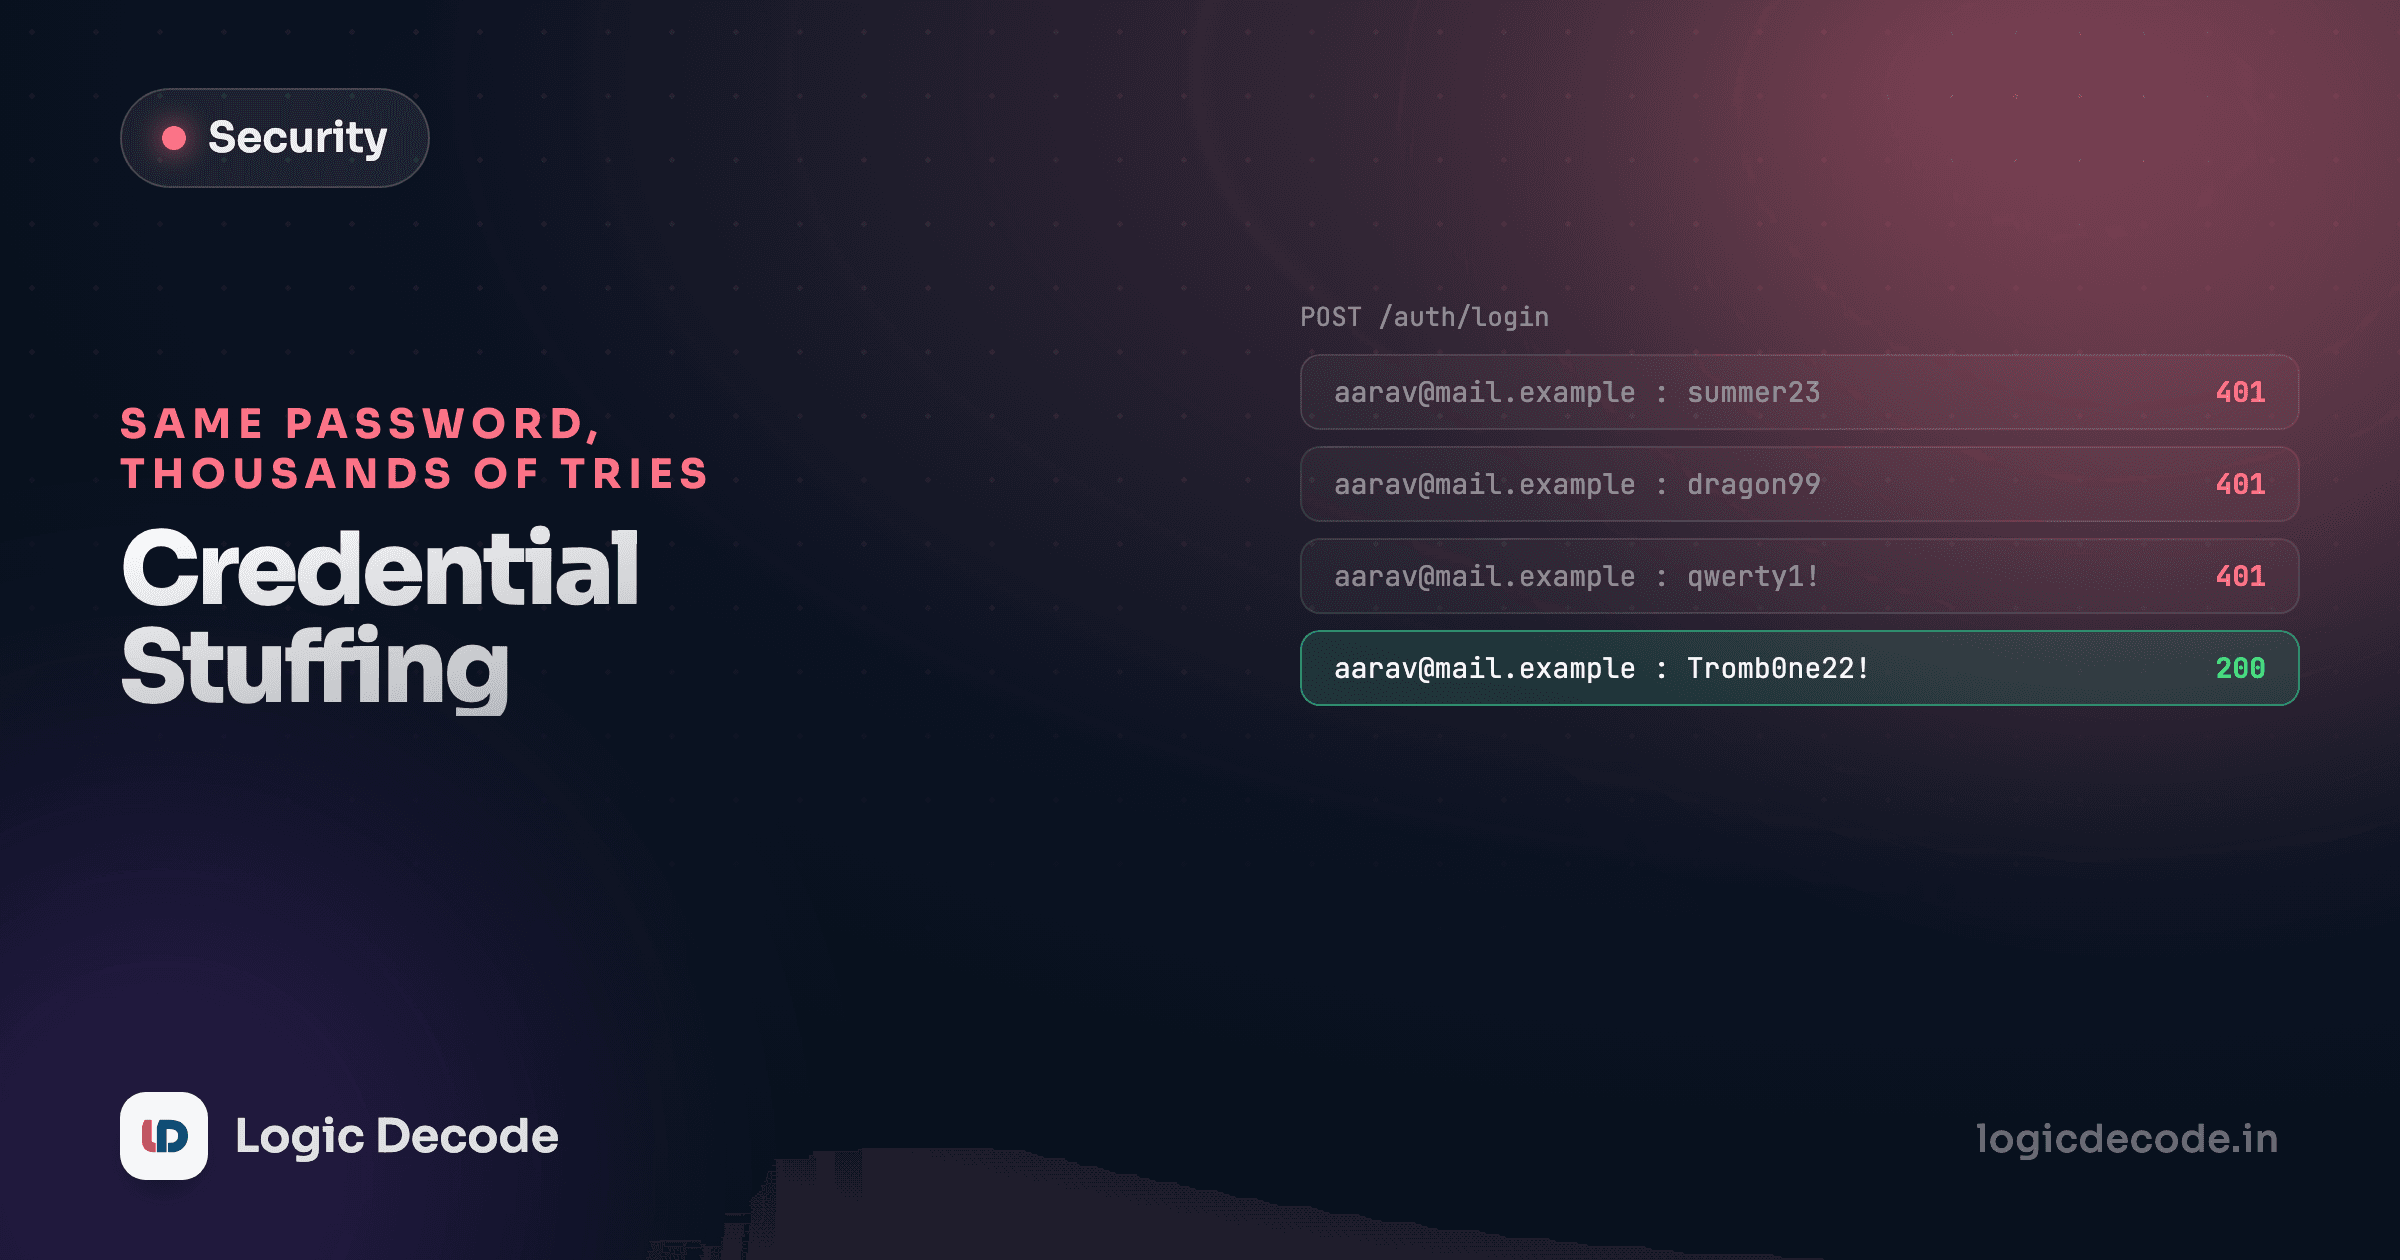
Web DevBreaking authenticationCredential stuffing, brute force, and the timing bug that leaks which emails have accounts, with the real fix from a login endpoint in production.Sep 14, 2026·6 min
Web DevUser accounts and password hashing done rightWhy registerUser inserts first and catches the UNIQUE violation instead of checking first, and why verifyUser hashes a dummy password on every failed login.Sep 4, 2026·7 min
Web DevAuthentication: sessions vs JWTHow Linkstash's opaque session tokens actually work end to end, and the real tradeoff against JWTs: revocability versus a database lookup on every request.Sep 3, 2026·6 min
 Web Dev