Web DevRate limiting, abuse and denial of walletA negative ?limit= that returns every row in a table, why SQLite treats it as no limit at all, and the real clamp that fixes it in Linkstash.Sep 17, 2026·6 min
Web DevProject: attack and harden LinkstashA full security review pass over Linkstash's real endpoints, tying every fix from this series (SQLi, XSS, IDOR, timing, rate limits) into one checklist.Sep 17, 2026·6 min
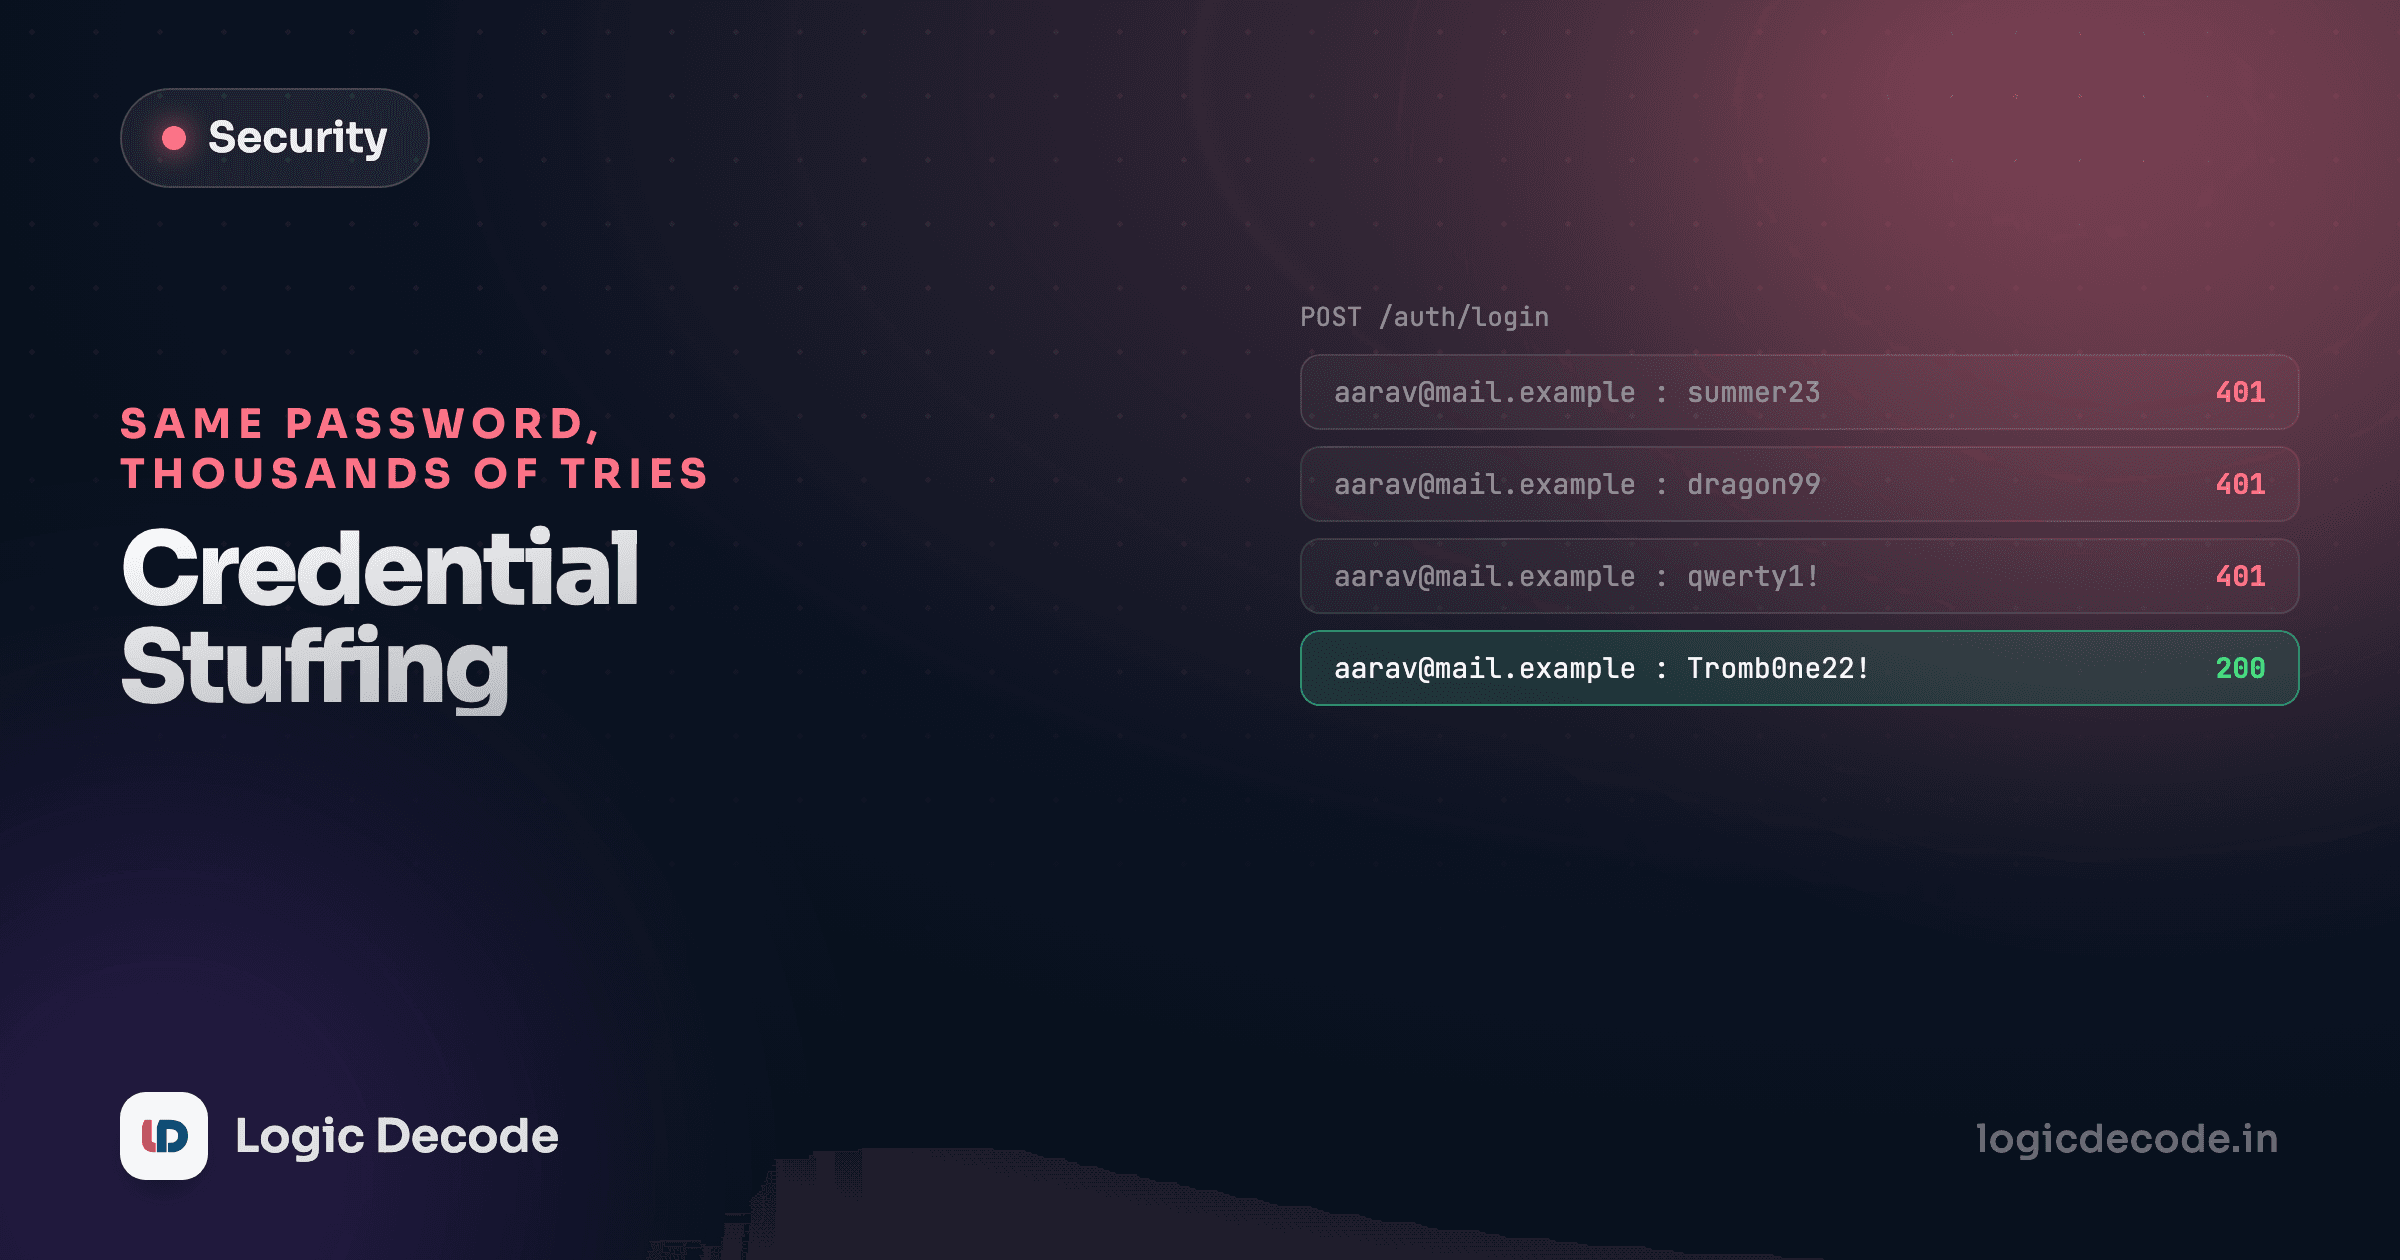
Web DevBreaking authenticationCredential stuffing, brute force, and the timing bug that leaks which emails have accounts, with the real fix from a login endpoint in production.Sep 14, 2026·6 min
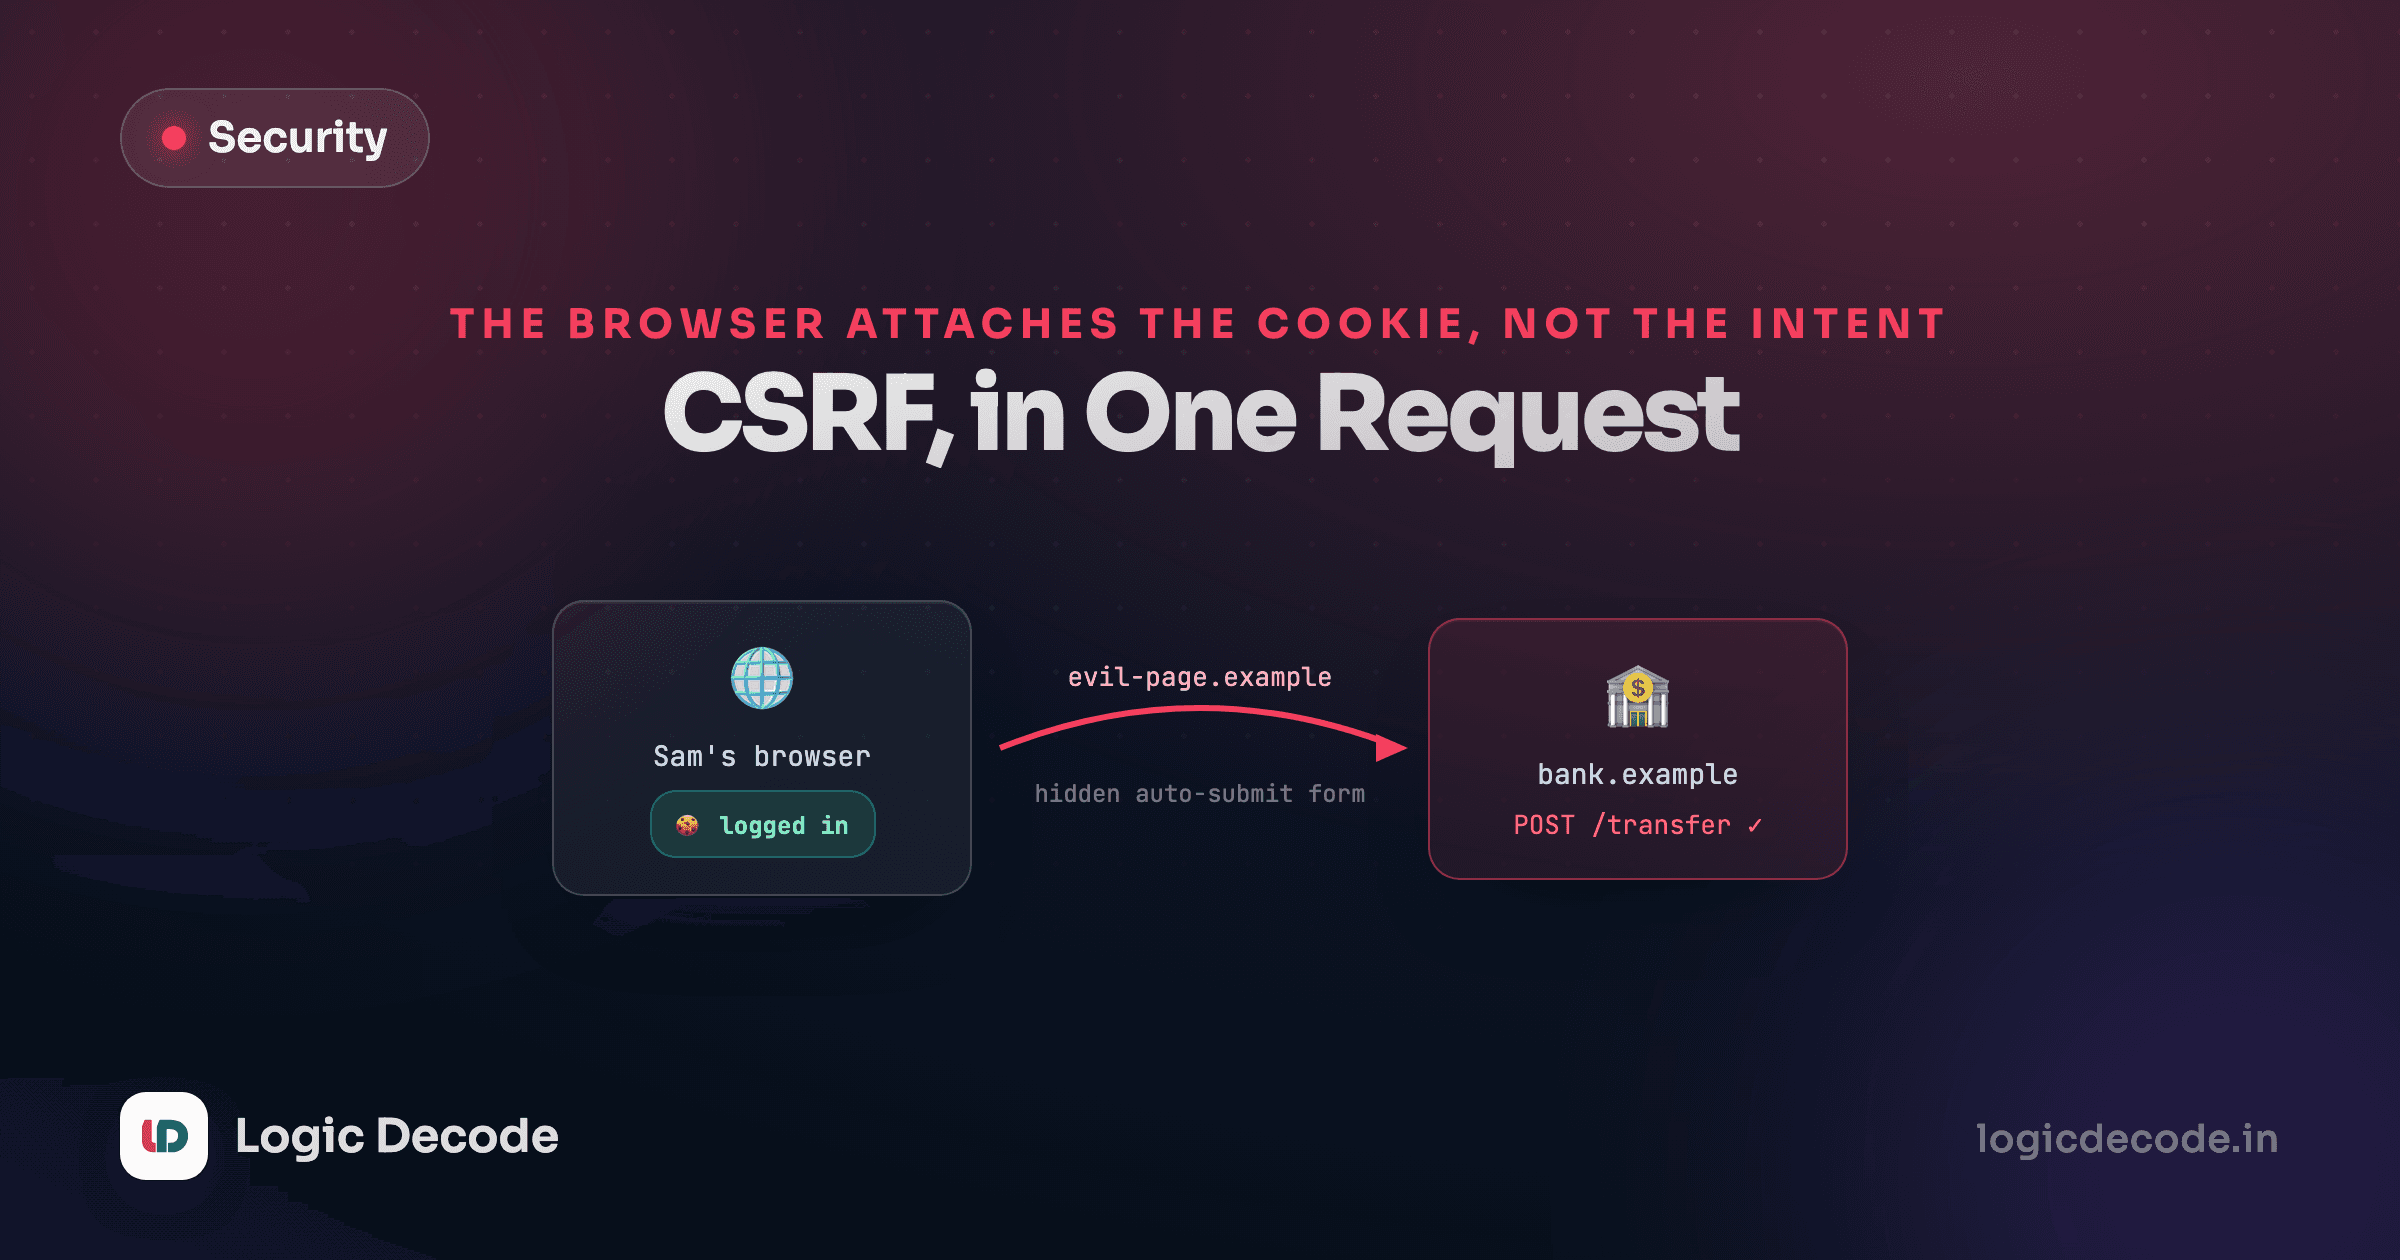
Web DevCSRF: making the browser betray its userHow cross-site request forgery uses a browser's own cookie-sending rules to trigger actions a logged-in user never asked for, and how to actually stop it.Sep 13, 2026·6 min
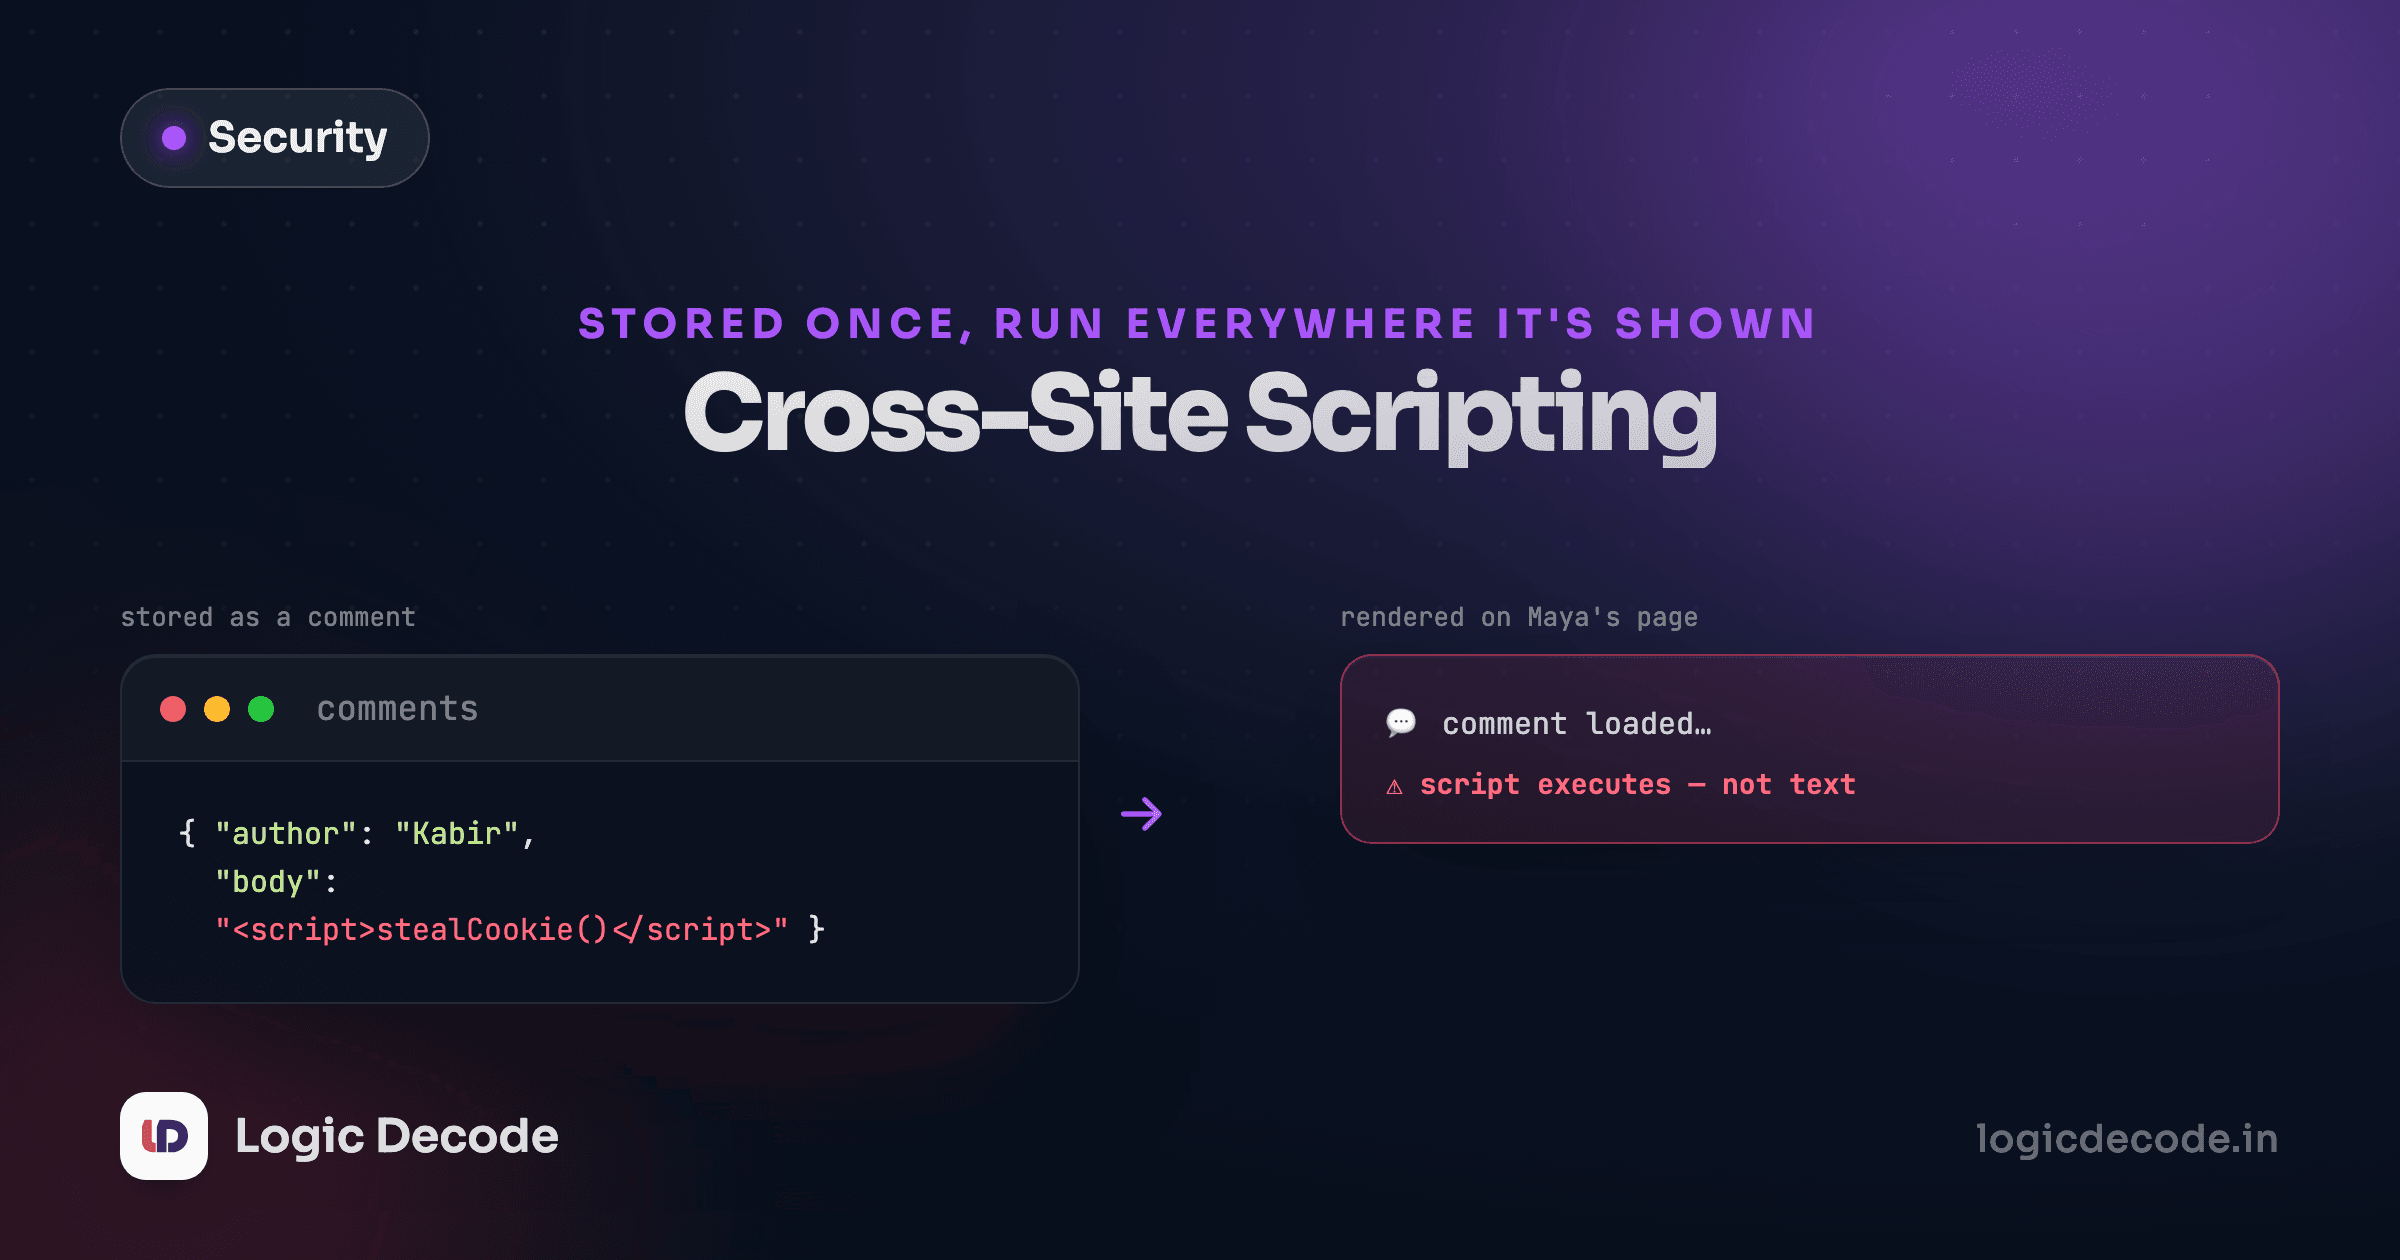
Web DevXSS: running your code on their pageHow cross-site scripting turns a comment box into a way to run JavaScript on someone else's session, demonstrated live, then fixed with proper escaping.Sep 13, 2026·6 min
Web DevSQL injection: break it live, then fix itRun a real SQL injection against a real in-browser SQLite database, watch every row come back, then fix it the way Linkstash actually does.Sep 12, 2026·6 min
Web DevHow apps actually get brokenA working threat model for web apps: who attacks them, what they're after, and the shape every lesson in this security series follows.Sep 12, 2026·5 min
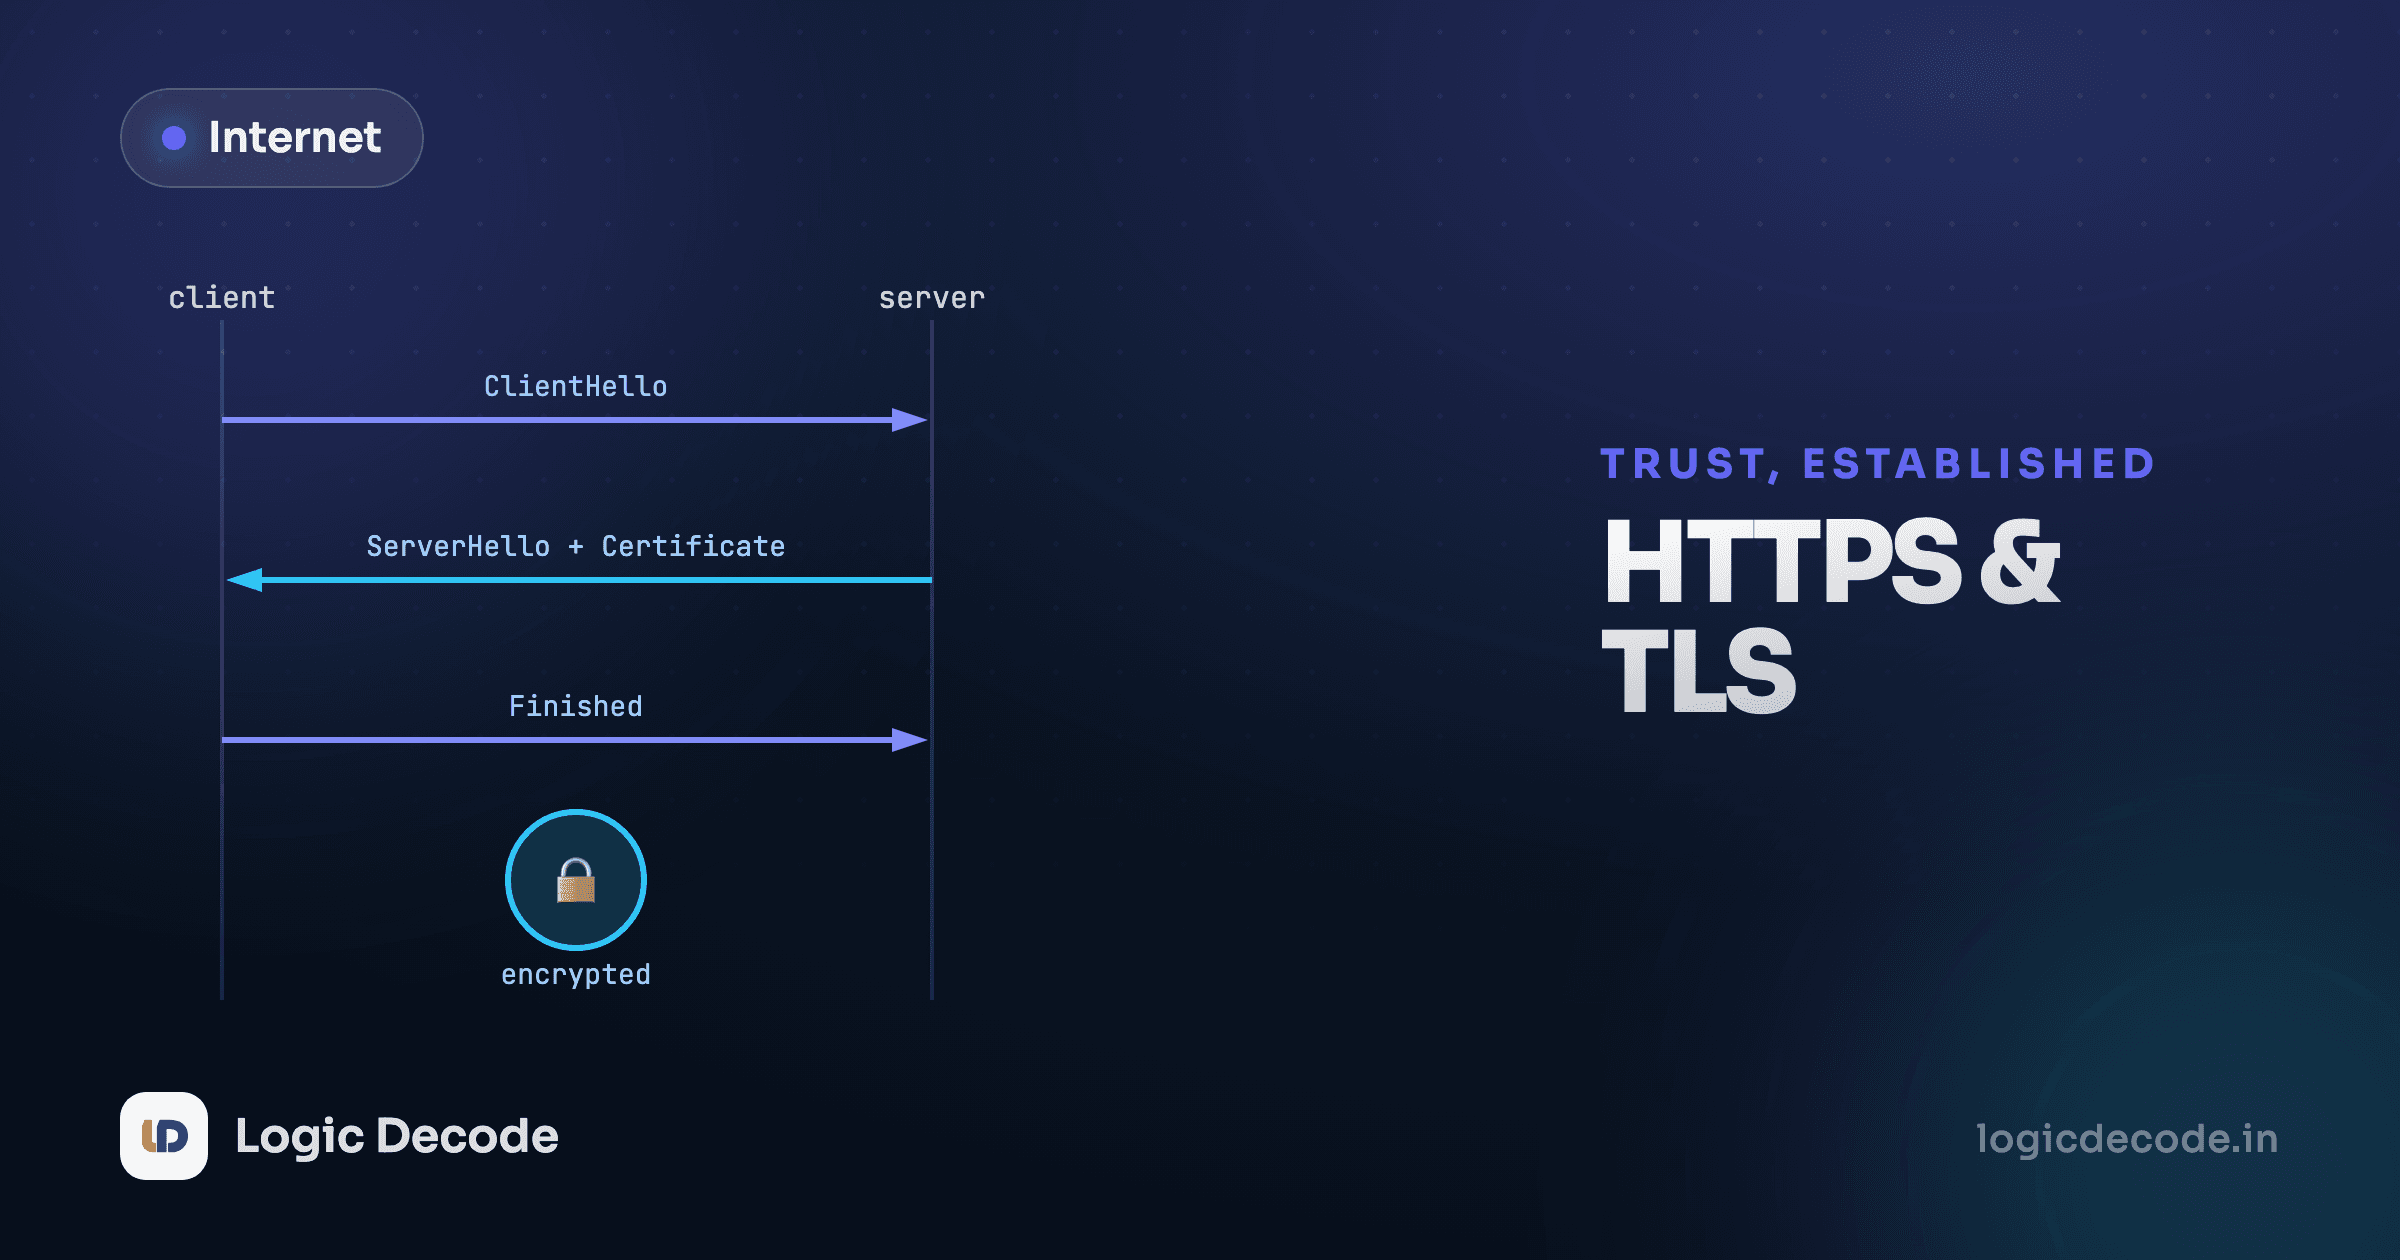
CSHTTPS and TLS: how the padlock worksHow TLS encrypts a connection, why TLS 1.3 needs one round trip instead of two, and what the browser padlock does and doesn't protect.Aug 27, 2026·6 min
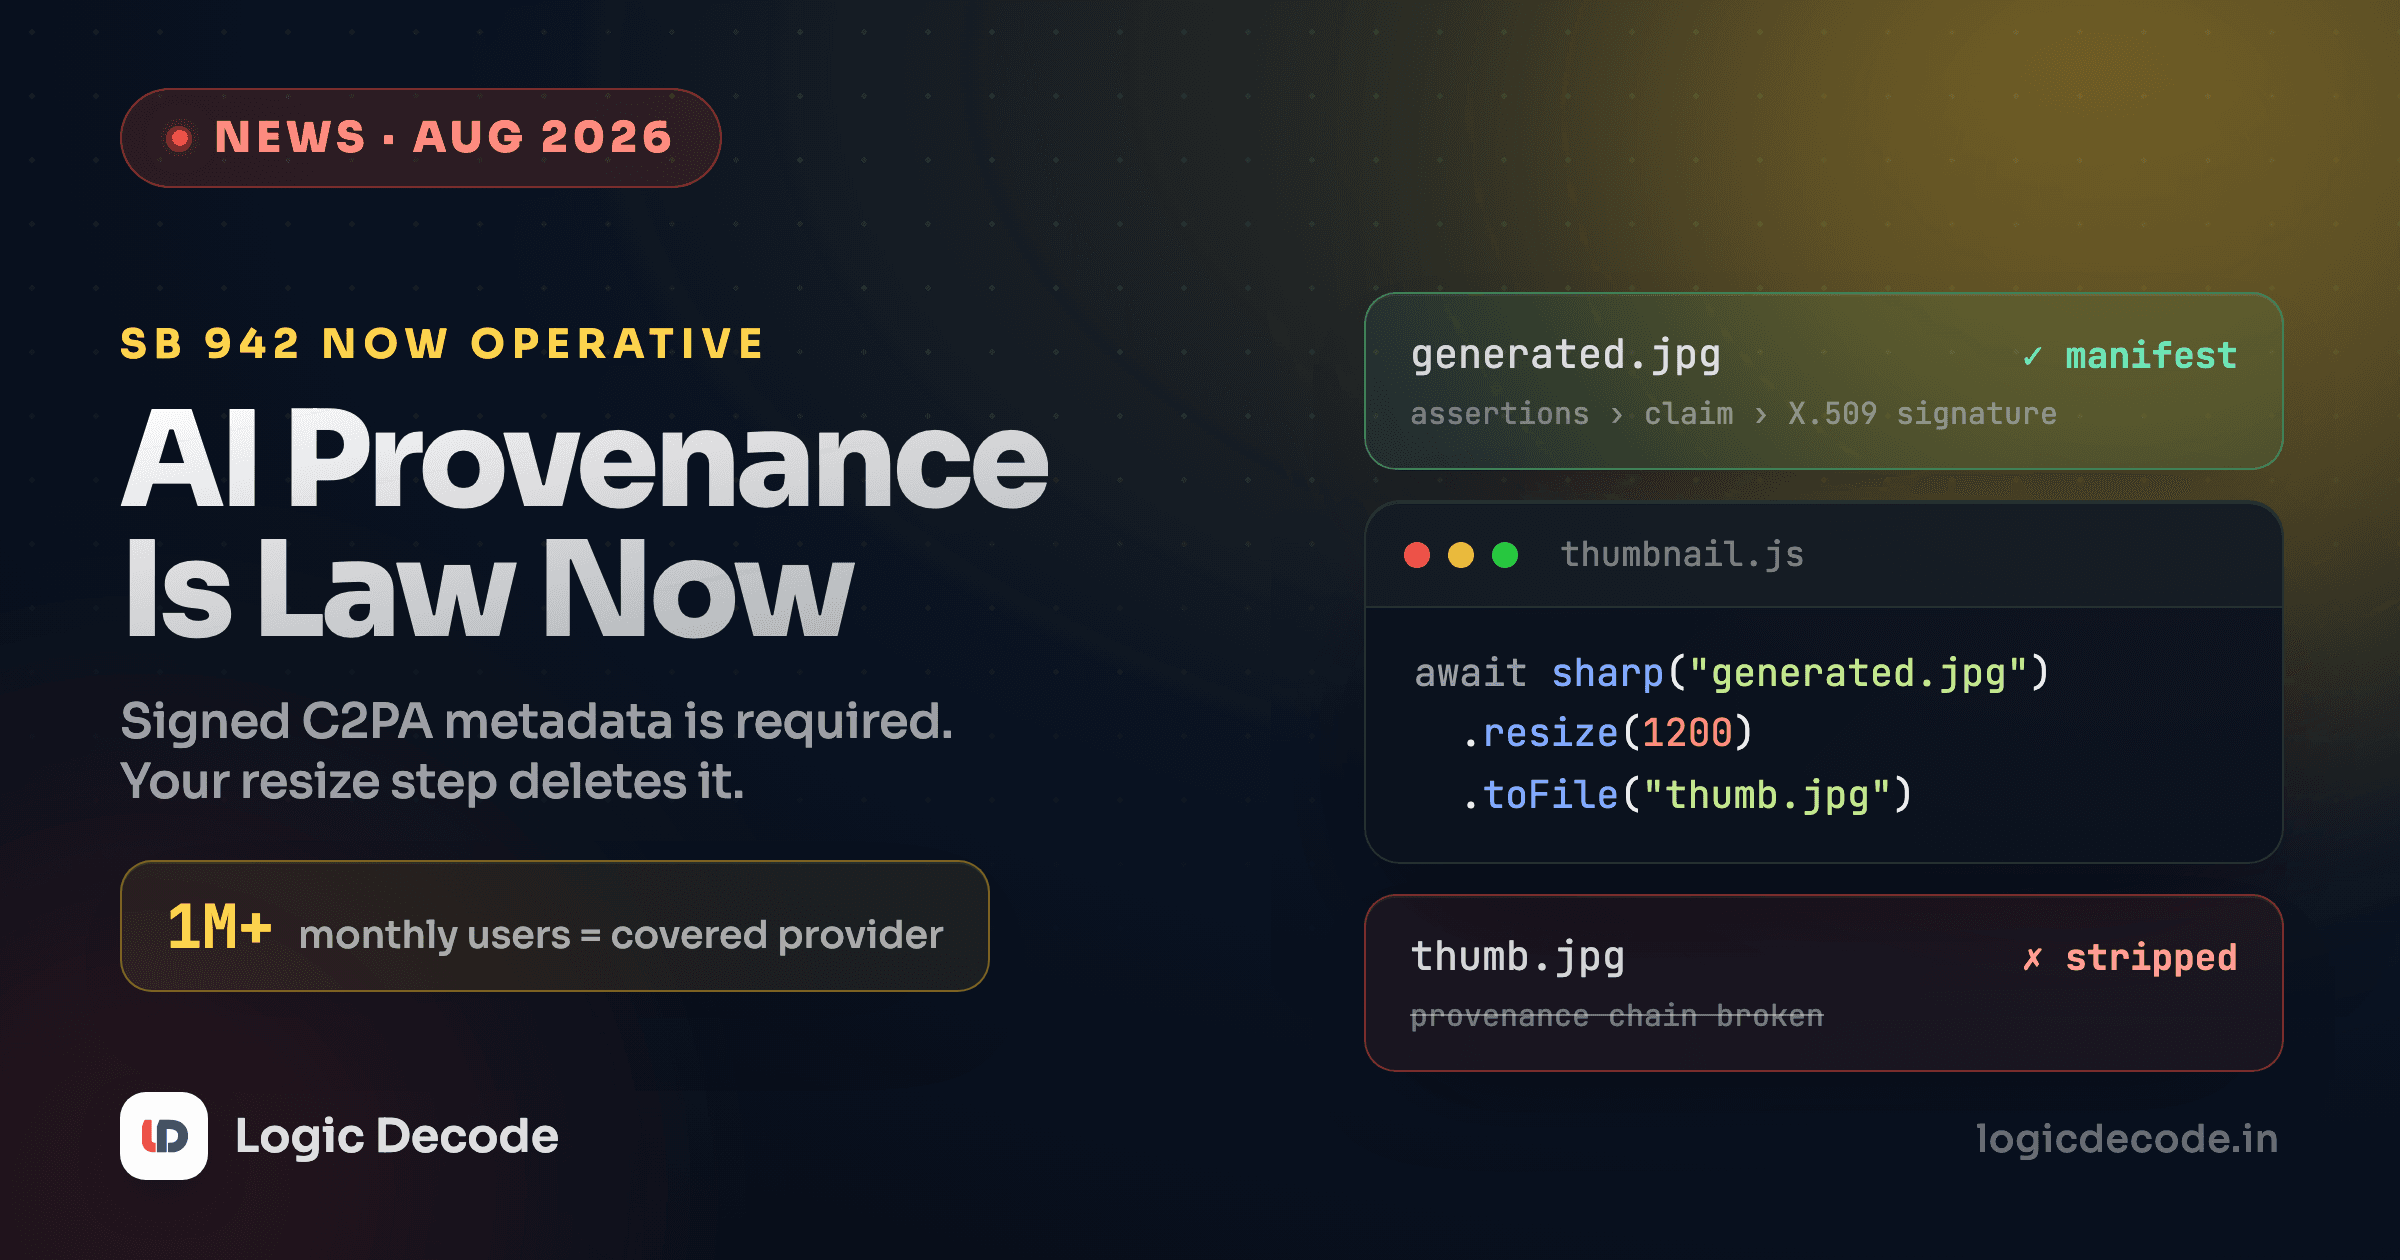
NewsCalifornia's AI Transparency Act Is Live: C2PA ExplainedSB 942 became operative August 2, 2026. What covered providers must ship, how C2PA provenance works, and why most image pipelines quietly break it.Aug 19, 2026·8 min
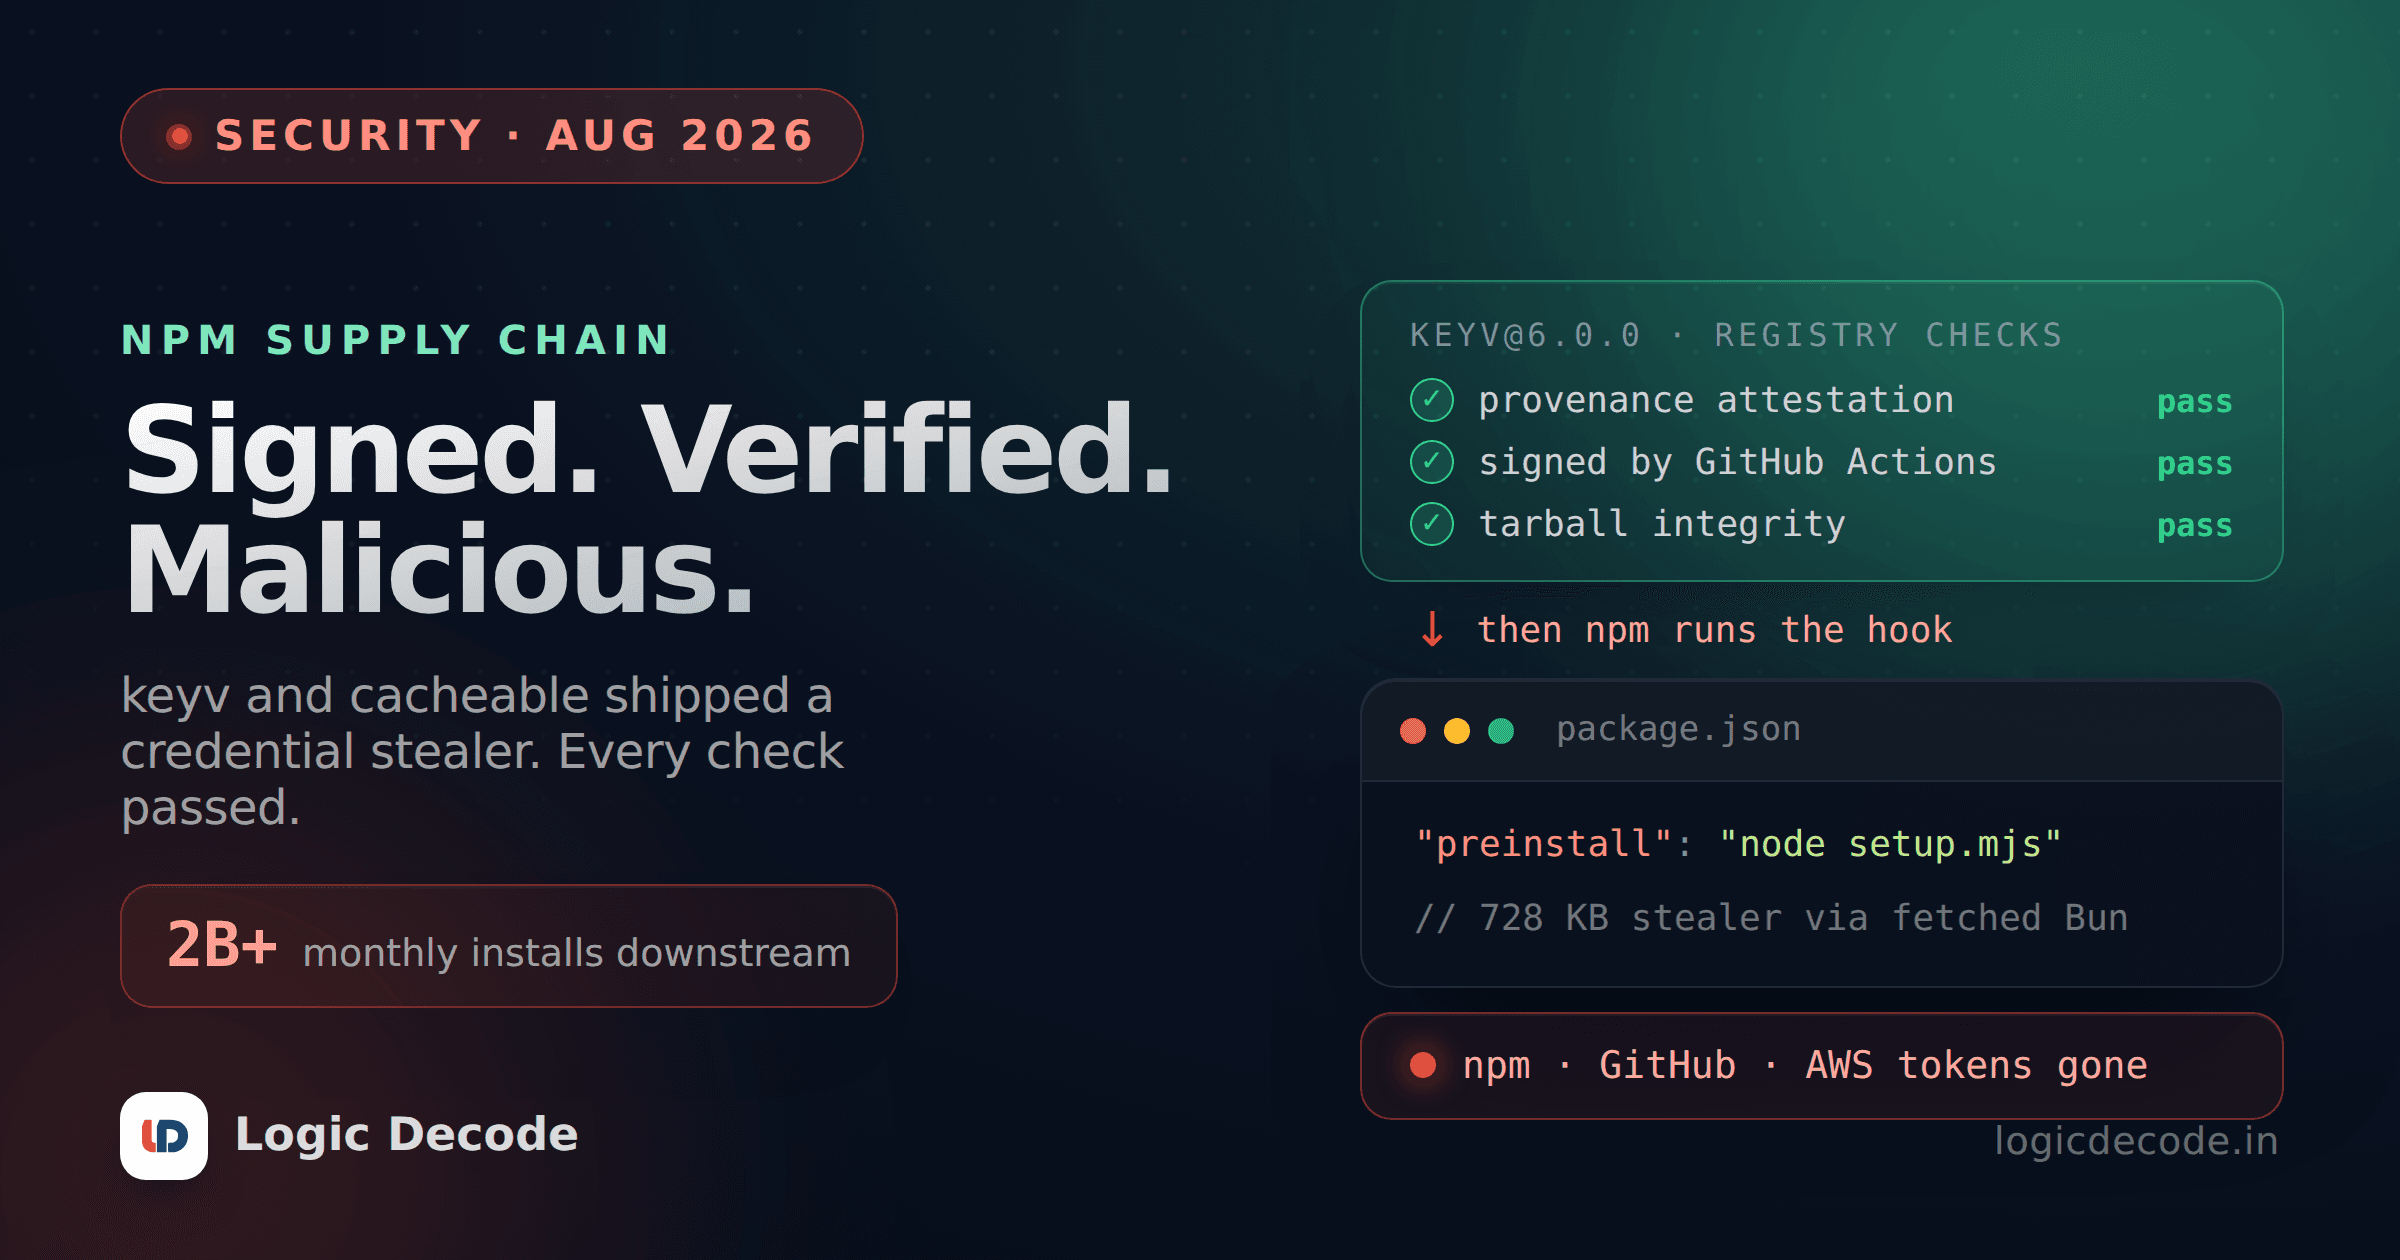
NewsThe keyv npm Attack: Signed, Verified, and MaliciousThe keyv and cacheable npm packages shipped a credential stealer with valid provenance. What it did, how to check if you're hit, and what to fix first.Aug 7, 2026·9 min
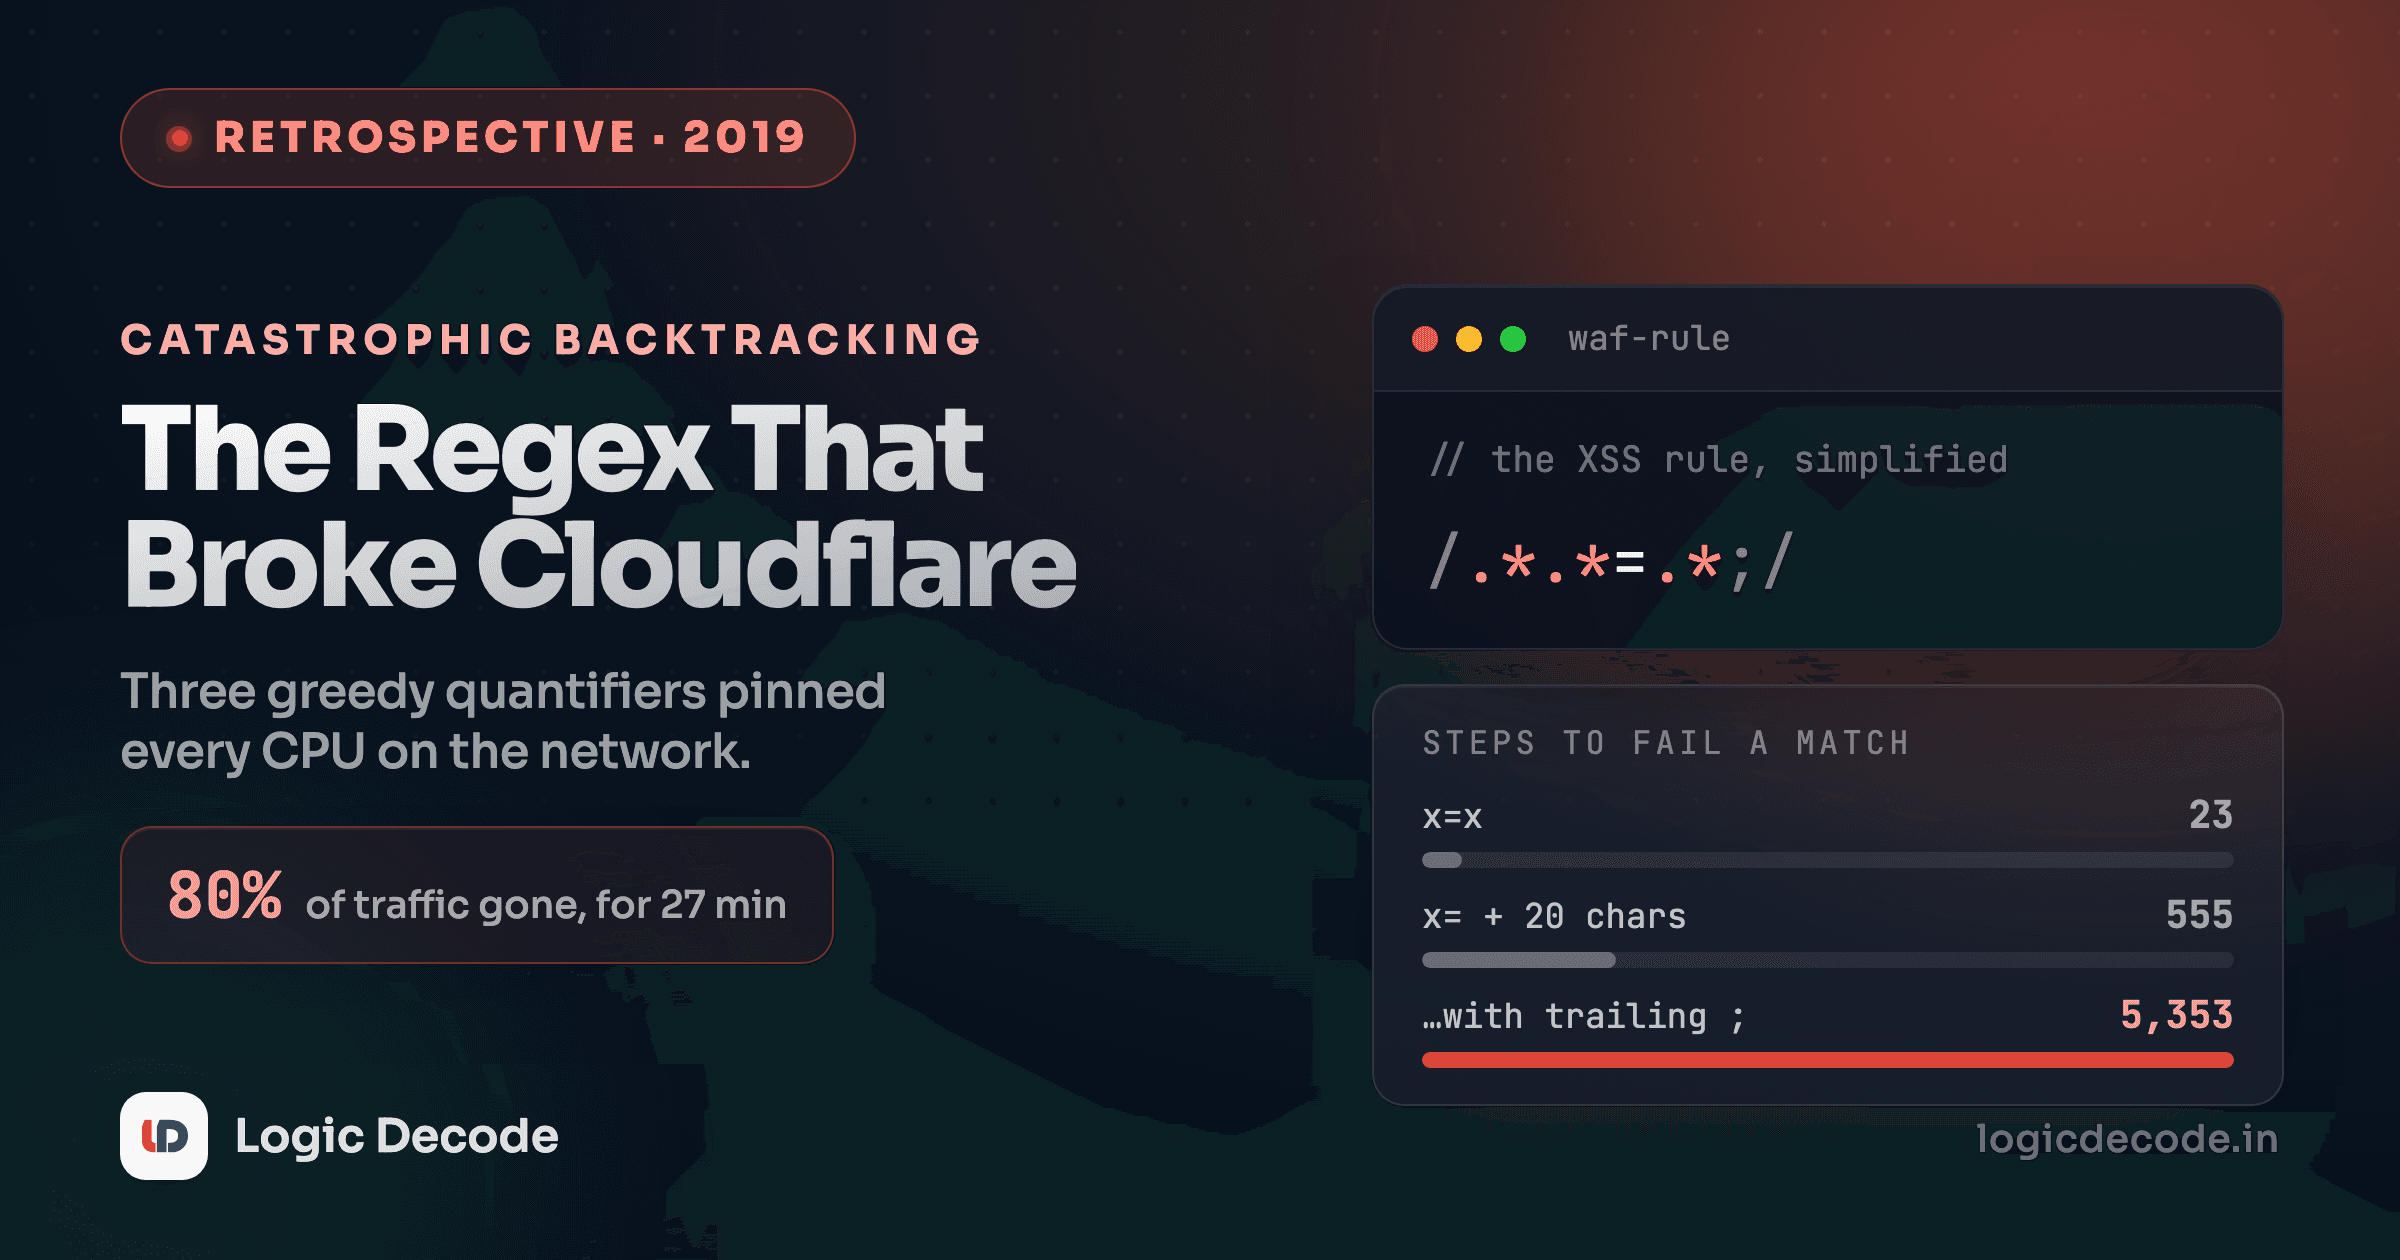
NewsThe Regex That Broke Cloudflare: ReDoS ExplainedOne regex dropped 80% of Cloudflare's traffic in 2019. How catastrophic backtracking works, how to spot it in your code, and the deploy lesson behind it.Jul 30, 2026·11 min
NewsPrompt Injection: The #1 Security Risk for AI AppsPrompt injection is the top vulnerability in LLM apps. See how the attack works, why AI agents make it worse, and how to actually defend your code.Jun 28, 2026·7 min
 Web Dev